Access that ends on its own.
Short-lived, policy-checked access for people and workloads, with the credentials that must remain vaulted and rotated.
- RequestPick the safe or account and say how long.
- ApproveAn approver for the safe, or an Admin, decides.
- ConnectThrough Zerostand, which supplies the credential.
- ExpiresThe grant ends; open sessions are cut within 30 seconds.
One platform to end standing privilege
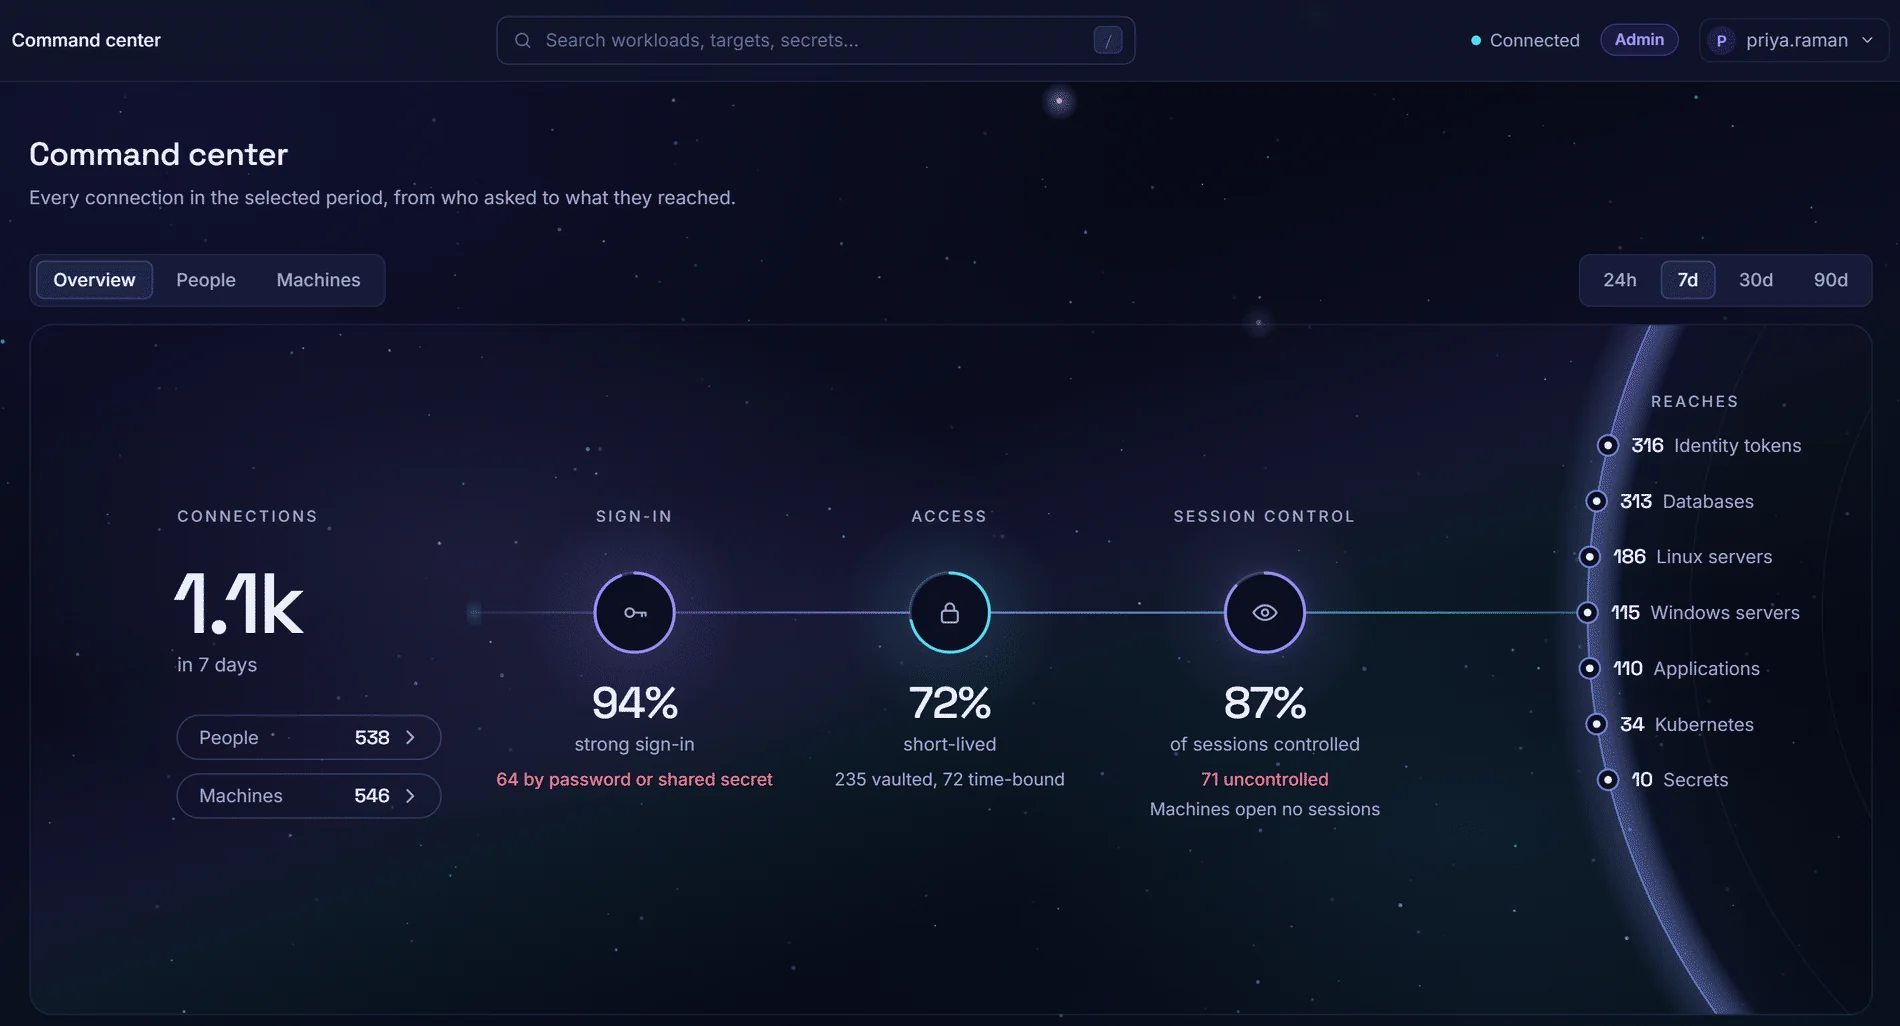
Zerostand gives every identity short-lived, policy-checked access to servers, databases and applications, and takes it back when the time is up.
People
Sign in with your identity provider and MFA. Reach servers, databases and apps by name, through a grant whose window closes on its own.
Learn more →Workloads
Prove identity with what their platform already gives them. With platform attestation no secret is shipped first, and every identity credential they receive expires.
Learn more →Vaulted accounts
The logins you cannot remove yet live in safes, rotated on a schedule, verified to still work and reconciled when they drift.
Learn more →Privileged access management was first built to store credentials for a few administrators. Today every service and pipeline needs privileged access, and a stored credential stays a liability until it is rotated.
Sources
- Verizon, 2025 Data Breach Investigations Report, 23 April 2025: "third-party involvement in breaches has doubled to 30%".
- Verizon, 2025 Data Breach Investigations Report, 23 April 2025: "credential abuse (22%) and exploitation of vulnerabilities (20%) continue to be the leading initial attack vectors".
- GitGuardian, The State of Secrets Sprawl 2026: tracking valid secrets detected in public repositories in 2022, "Four years later, 64% are still active and exploitable".
The zero-standing-privilege control plane
Every access, human or machine, follows the same three steps. Nothing reaches a target without proving who it is and passing policy; wherever the target allows, it receives a credential that will expire.
- ◯People
- ▣Workloads
Prove
- IdP sign-in with MFA
- Kubernetes and cloud attestation
- OIDC from CI
- Step-up MFA per target
Decide
- Policy as code
- Approval chains
- Access windows
- Ticket and reason where you require them
Lease
- Short-lived credential
- Brokered, recorded session
- Expires on its own
- Grants, approvals and sessions in the audit log
- ▤Servers
- ◫Databases
- ⬡Kubernetes
- ▭Web apps
Every control, one console
The capabilities a privileged-access programme needs, built together rather than bolted on.
Zero standing privilege
Short-lived tokens, one-time database logins, SSH certificates, brokered RDP. Every grant, certificate and token Zerostand issues has an expiry; vaulted passwords keep rotating.
Learn more →Workload identity
A service proves what it is with the identity its platform already gives it. Trust rules enrol a fleet; the Go client refreshes credentials before they expire.
Learn more →Approvals that expire
Multi-step chains, access windows, ticket references, MFA step-up, and break-glass limited to named people and capped in time.
Learn more →Credential rotation
Safes, platforms and policies. Rotate on a schedule, verify the login still works, reconcile when the target drifts.
Learn more →Session recording
SSH, RDP, database and web sessions brokered through Zerostand; SSH, RDP and web sessions recorded by default. Live view for SSH; end an open session.
Learn more →Discovery and governance
Find accounts outside any safe, run recertification campaigns, walk the access graph, and export the evidence an auditor asks for.
Learn more →See the full access lifecycle
A 30-minute walkthrough with an engineer on our demo environment. Bring your use cases; we map them to your environment, and a proof of value then runs it on your own servers.
- A person connecting to a server with an SSH certificate that expires
- A one-time database login, approved in context, its statements logged, revoked at the hour
- A workload attesting with its Kubernetes identity and receiving a credential
- A vaulted account rotated, verified and reconciled while you watch
Request sent.
We will reply from a named engineer, usually within one working day, with a few times to choose from.
Don't take our word for it
Test it on your systems, check our mappings, read how we secure it.
Prove it on your systems
A four-week proof of value on your servers and a database, against criteria we agree in writing first. You keep the evidence.
Proof of value →Check our control mappings
ISO/IEC 27001, the AICPA Trust Services Criteria, NIST SP 800-53, PCI DSS, HIPAA, DORA, NIS2 and Asia-Pacific regulators: see which controls Zerostand supports and what evidence your team can produce.
Compliance mappings →Read how we secure it
Deployment, key custody, audit integrity, availability, and what is still on the roadmap, stated plainly.
Trust and security →Questions buyers ask first
Does Zerostand replace our password vault?
It removes standing credentials wherever a short-lived one can be issued instead, and vaults, rotates and verifies the accounts that must remain. You can start with one safe.
Do we need to install agents on every target?
No. Targets are reached over the protocols they already speak: SSH, WinRM, and the native database wire protocols. Linux servers need one sshd setting to trust the Zerostand certificate authority.
Where does it run?
As containers on infrastructure you control, on-premises or in your cloud. Zerostand is self-hosted: secrets are stored and used on infrastructure you control and are never sent to us. Data goes elsewhere only to destinations you configure, such as your SIEM, email server or ticketing system.
What happens if the control plane is down?
Run it as an active and a standby node on PostgreSQL. For the worst case, a sealed offline export of the break-glass accounts, encrypted to keys your security team holds.
How are machines and services handled?
As identities, under the same policy and audit as people. A workload attests with its Kubernetes or cloud identity and receives a credential that expires.